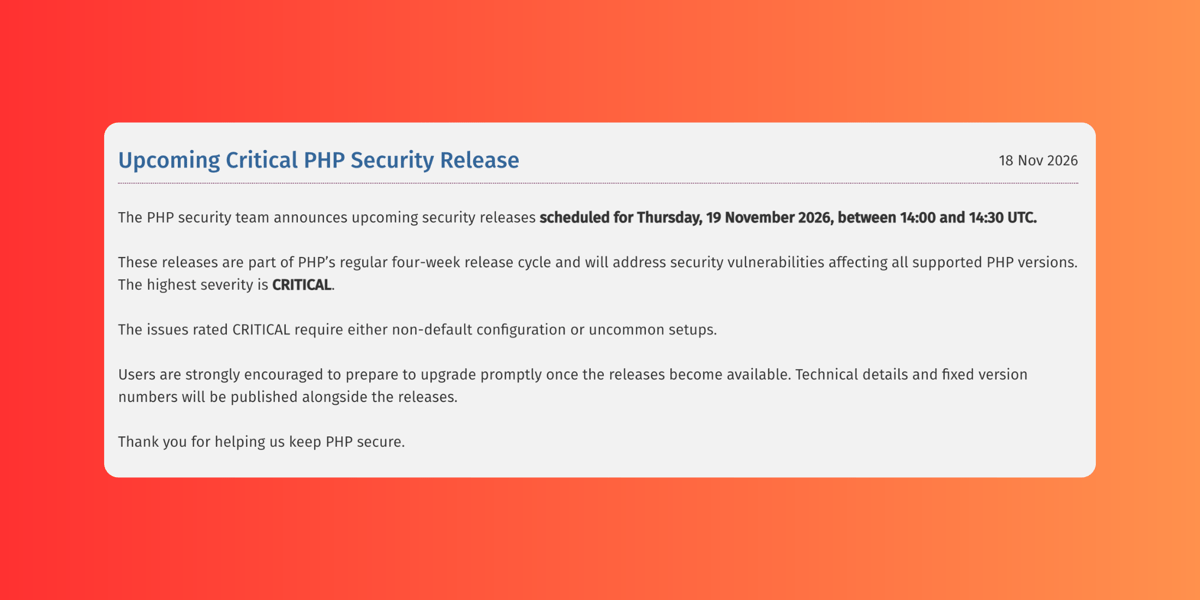
Today’s PHP release fixes CVE-2026-126714, a critical (9.2) remote code execution bug in the default file-based session handler. It’s the follow-up to last month’s PHP2Shell fix.
Yuhang Wu, a security researcher at depthfirst:
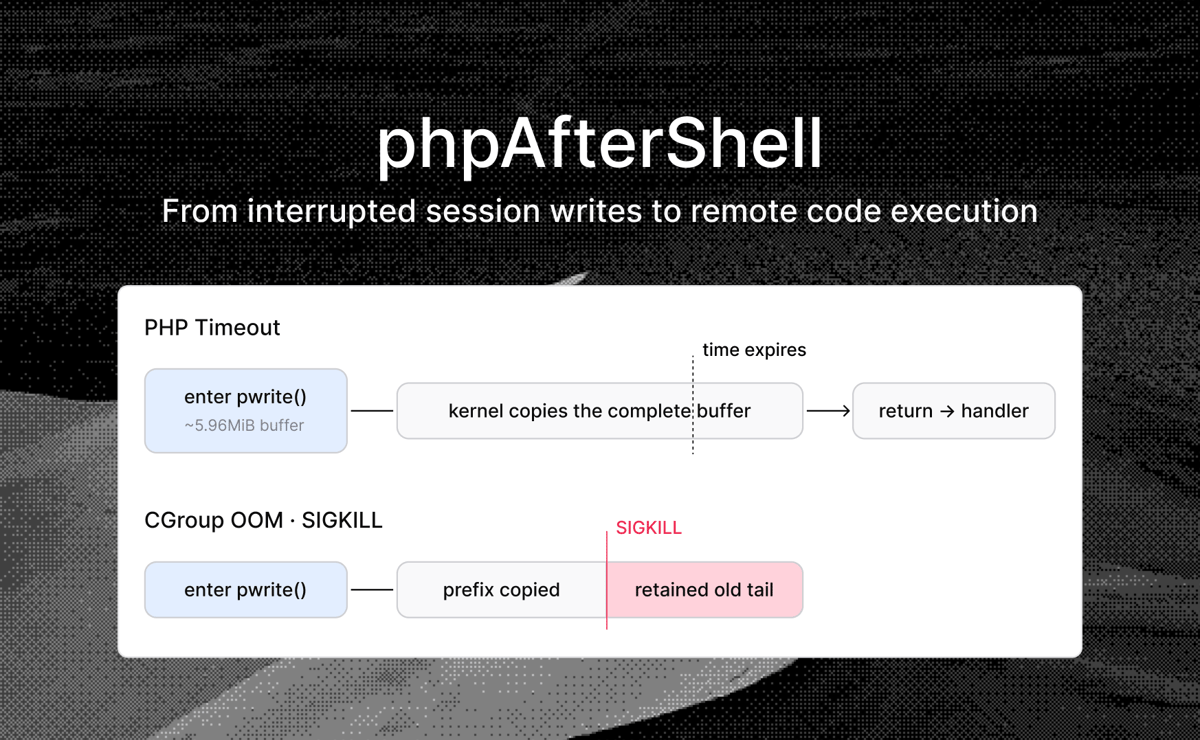
PHP can update a file-backed session while parsing an unauthenticated multipart request, even before the target script begins execution. We discovered reliable methods to interrupt the file operation during session upload-progress updates, allowing us to splice the prefix of one valid session with the suffix of another. A subsequent session operation treats the corrupted data as legitimate server-side state, giving attackers control over session values and the ability to trigger object deserialization. By chaining this primitive with a memory-corruption in a PHP-native class, we achieved remote code execution. We reported this vulnerability to the PHP team, and it was assigned CVE-2026-126714, with a critical CVSS score of 9.2.