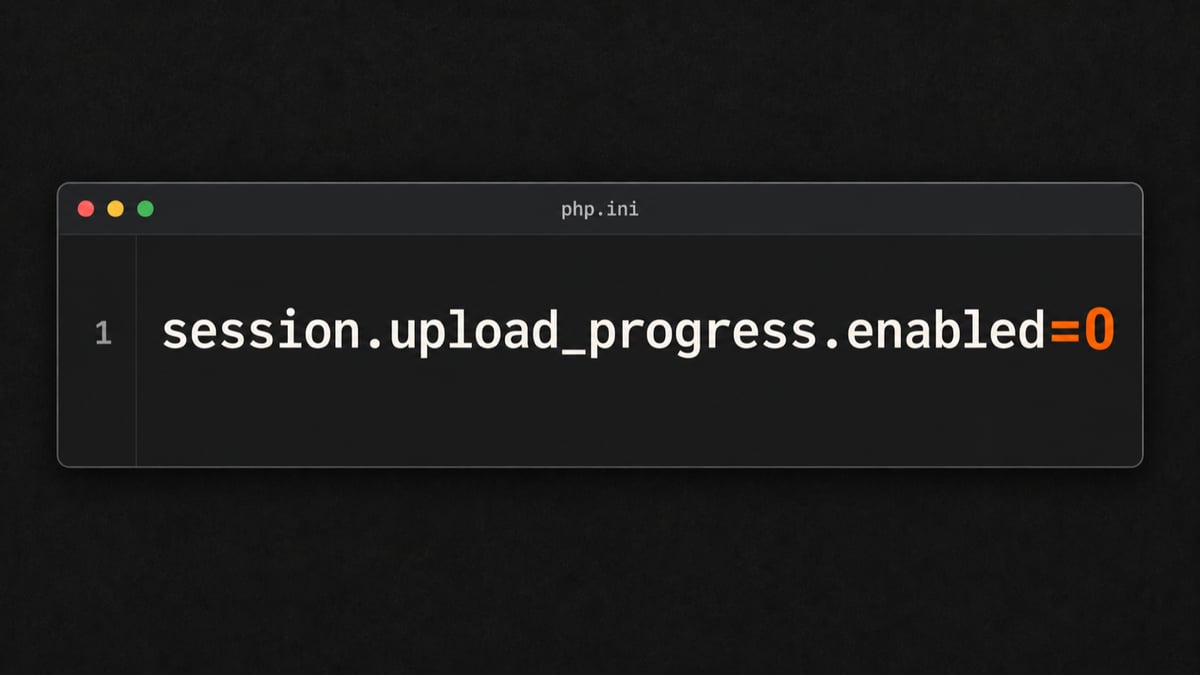
The PHP security team just posted an informational advisory on php.net about session upload progress. It suggests you set session.upload_progress.enabled=0 until the next regular bugfix release, "to fully protect from an unlikely RCE vector."
This comes two days after the critical PHP release that fixed two remote code execution bugs. The team is tracking this one as a new CVE, CVE-2026-115560, and says it will publish a full advisory with the next release.
Who Is Affected
The team says the issue "can only occur under an unusual combination of configuration and application code." All three of these have to be true:
- Your configuration sets
session.serialize_handlertophp_binaryorphp_serialize. - Your app switches it back to
phpat runtime withini_set()before it callssession_start(). - Session upload progress is still enabled.
If your app never changes the serialize handler at runtime, you can leave session upload progress on. Because the setup is so unlikely, the team is fixing it in the regular release cycle instead of shipping another emergency release.
What You Should Do
If you already turned off session upload progress after the October 21 advisory, keep it off. The team says no further action is needed.
That setting was already on the list of mitigations in GHSA-6wmf-4rv5-p3rp, the advisory for CVE-2026-109619. If you haven't applied it yet and your app matches the pattern above, the earlier advisory has the details that still apply:
- Set
session.upload_progress.enabled=0inphp.ini, an FPM pool, or the server config. - Don't rely on
ini_set()or a.user.inifile, because they apply too late. - Restart every worker so the change takes effect.
You still need the October 21 updates either way. PHP 8.5.12, 8.4.27, 8.3.36, and 8.2.35 fix the two critical bugs, and this setting doesn't replace them.
Read More
Read the informational advisory on php.net, and catch up on the rest of the story in the PHP Foundation's account of the release.